Security audits
A clear, honest picture of how secure your business really is.
We review the controls that protect your software, cloud accounts, and day-to-day operations, then tell you plainly what is working and what is not. The result is a prioritised improvement plan rather than a pile of findings with no direction.
- Secure code review
- Cloud configuration review
- Access and identity controls
- Practical, prioritised roadmap
Beyond the perimeter
Security depends on more than one strong wall.
Most incidents do not come from a single dramatic flaw. They come from a combination of small things: an old admin account nobody removed, a storage bucket left public after a demo, a library that has not been updated in years, a backup that has never been restored. A security audit looks across all of these layers at once, so you see how they add up.
Our audits combine document review, interviews with your team, and hands-on inspection of code, configuration, and logs. We measure what we find against recognised good practice, explain each gap in plain terms, and estimate the effort to close it. You come away knowing where you stand and what to do next, in order.
Audit scope
Every layer that keeps your systems safe.
Audits can cover your whole organisation or focus on a single product or environment. We tailor depth to your size and risk.
01 Secure code review +
- SAST
- Secrets detection
- Input validation
- Cryptography
- Code patterns
Manual and tool-assisted review of your source code for insecure patterns, unsafe input handling, weak cryptography, and hard-coded secrets.
02 Cloud configuration review +
- CIS Benchmarks
- IAM
- Logging
- Encryption
- Public exposure
Your AWS, Azure, or Google Cloud accounts checked against benchmark settings for identity, logging, storage, encryption, and network exposure.
03 Identity and access review +
- MFA
- Privileged access
- SSO
- Account lifecycle
- Access reviews
Who can access what, and why: user accounts, admin rights, service credentials, MFA coverage, and joiner-mover-leaver processes.
04 Dependency and supply chain review +
- SCA
- SBOM
- Container images
- CI/CD security
- Licences
Third-party libraries, container images, and build pipelines assessed for known vulnerabilities, outdated components, and tampering risk.
05 Infrastructure and endpoint review +
- Patching
- Hardening
- Remote access
- Endpoint protection
Servers, workstations, and network devices reviewed for patch levels, hardening, remote access, and endpoint protection.
06 Operational security review +
- Logging
- Monitoring
- Backups
- Incident response
- Change control
Logging, monitoring, backup, incident response, and change management examined to see whether you would detect and recover from an attack.
07 Audit report and roadmap +
- Risk ratings
- Executive summary
- Roadmap
- Effort estimates
A risk-rated report with an executive summary, detailed findings, and a phased roadmap with effort estimates for each fix.
What you gain
Know where you stand, and what to fix first.
-
A single view of risk
Code, cloud, and operations assessed together, so nothing falls between teams.
-
Spend where it counts
A prioritised roadmap stops budget going on low-value fixes.
-
Stronger foundations
Gaps in access, logging, and backups closed before they become incidents.
-
Easier due diligence
A recent independent audit answers investor and customer questions quickly.
-
Measurable progress
A baseline you can re-audit against to show improvement over time.
-
Want to know where to begin? Book a free consultation and we will suggest the right audit scope for you.
Request a security audit →
Why Agleam Labs
Auditors who understand engineering trade-offs.
Hover or tap a card to see what it means in practice.
How we work
A structured audit with no disruption.
-
01
Plan
We agree scope, the systems and people involved, read-only access, and the standards we will measure against.
-
02
Gather
We review documents, interview key staff, and collect configuration, code, and log evidence.
-
03
Analyse
We test controls against good practice, verify findings, and rate each one by likelihood and impact.
-
04
Report and plan
We present the findings and agree a phased remediation roadmap with your team.
Agleam Labs in numbers
- Enterprise apps delivered
- 50+
- Enterprise apps delivered
- On-time delivery
- 99.8%
- On-time delivery
- Years of senior experience
- 10–30
- Years of senior experience
- Years of DevOps experience
- 20+
- Years of DevOps experience
- Technologies in production
- 20+
- Technologies in production
- Office, worldwide clients
- 1
- Office, worldwide clients
Standards and tooling
Measured against recognised good practice.
We benchmark your controls against established frameworks and use proven tools to gather evidence quickly.
- CIS Controls
- CIS Benchmarks
- NIST CSF
- OWASP ASVS
- ISO 27001
-
 AWS
-
 Azure
-
 Google Cloud
- SonarQube
- Semgrep
- Trivy
- Prowler
-
 GitHub Actions
-
 Docker
-
 Kubernetes
-
 Terraform
Industries
Security audits for growing and regulated businesses.
Organisations that hold sensitive data or run critical operations and need an objective view of their controls.
 FinTech
Payment, lending, and transaction platforms for always-on financial operations.
 Healthcare
Secure digital systems for data-heavy healthcare workflows and service delivery.
 Pharma
Compliant platforms for pharma operations, distribution, and regulated workflows.
 Real estate management
Property platforms for portfolios, leasing, tenants, sales, and day-to-day operations.
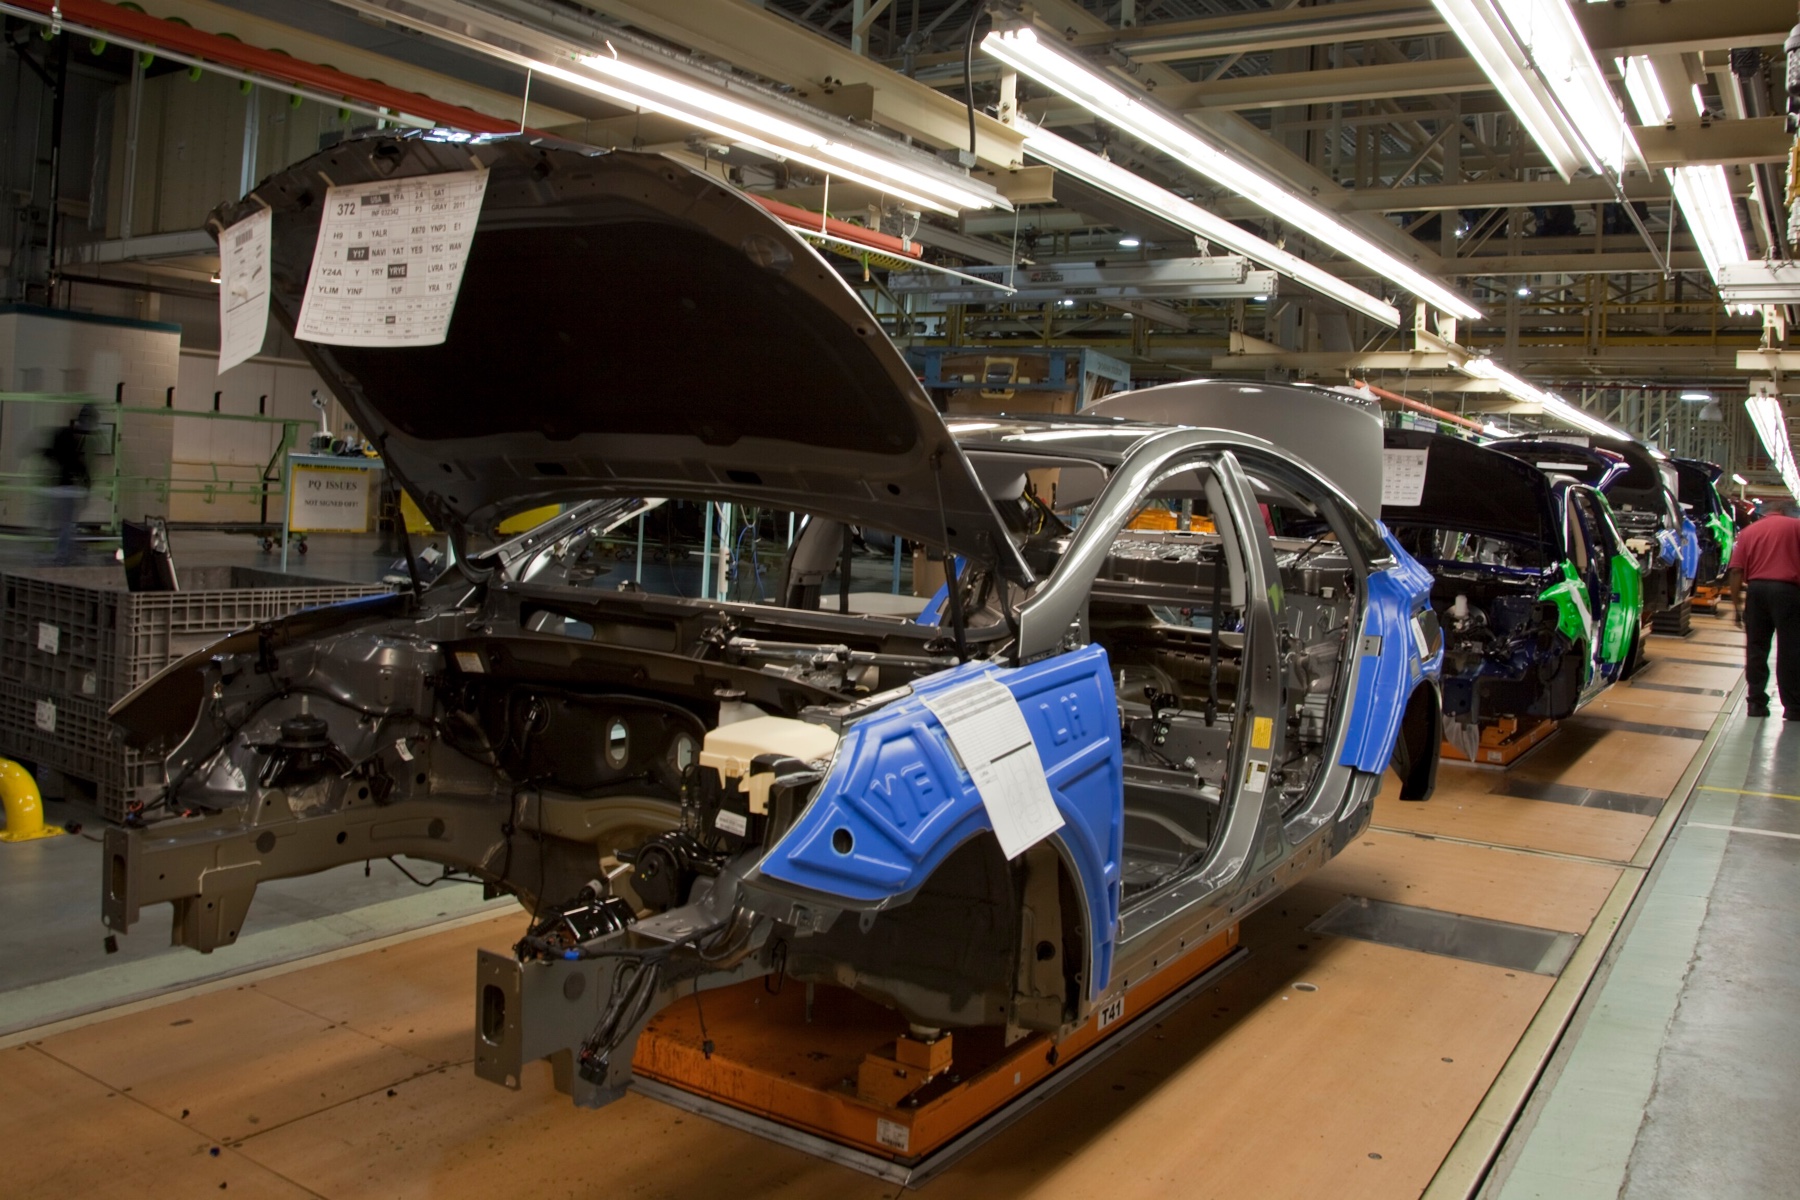 Manufacturing
Industrial software that connects production, inventory, quality, and plant operations.
 Logistics
Platforms for fleets, shipments, warehouses, and connected supply-chain operations.
FAQs
Security audits questions.
Straight answers about security audits with Agleam Labs.
Talk to an expert
Tell us what you are working on. A senior engineer will reply with honest advice and a suggested next step.
Book a call →How is a security audit different from a penetration test? + −
A penetration test tries to exploit weaknesses in specific targets. An audit is broader: it reviews whether the right controls exist across code, cloud, access, and operations, and whether they work as intended. Many clients start with an audit, then use penetration testing to verify the most exposed systems.
What access do you need? + −
Usually read-only access to the relevant cloud accounts and repositories, copies of key policies and diagrams, and time with the people who run your systems. We never need write access to production for an audit.
How long does a security audit take? + −
A focused audit of a single product or cloud environment typically takes two to three weeks. An organisation-wide audit covering several teams and platforms usually takes four to six weeks, depending on size.
Which standards do you audit against? + −
We commonly use CIS Controls and Benchmarks, the NIST Cybersecurity Framework, and OWASP ASVS, and can map findings to ISO 27001 or SOC 2 if you are preparing for either. We agree the reference standard during planning.
Will you help us fix what you find? + −
If you want us to. Some clients take the roadmap and work through it internally; others ask our engineers to implement the changes. Either way, we can re-audit later to confirm progress.
How do you keep our information confidential? + −
We sign an NDA before any access is granted, keep evidence in restricted storage, limit access to the audit team, and return or securely delete materials at the end of the engagement as agreed.
Start a project
Let's review your security controls.
- A free consultation with a senior engineer
- Clear scope, timeline, and budget
- Confidential, with an NDA on request
- Support after delivery
Prefer email?
info@agleamlabs.comFind out where your defences are thin.
Tell us about your systems and team. We will recommend an audit scope and send a clear proposal.